
Take an investment decision to the board.
Use FAIR-style quantification and calibrated scenarios to compare exposure with the cost and effect of treatment.
Exposure in decision languagePILLAR 2 OF 5 · EXPOSURE AND FORESIGHT
Anticipate brings asset, supplier, threat, vulnerability and scenario information into one risk picture—then quantifies the material exposure so leadership can choose a treatment.
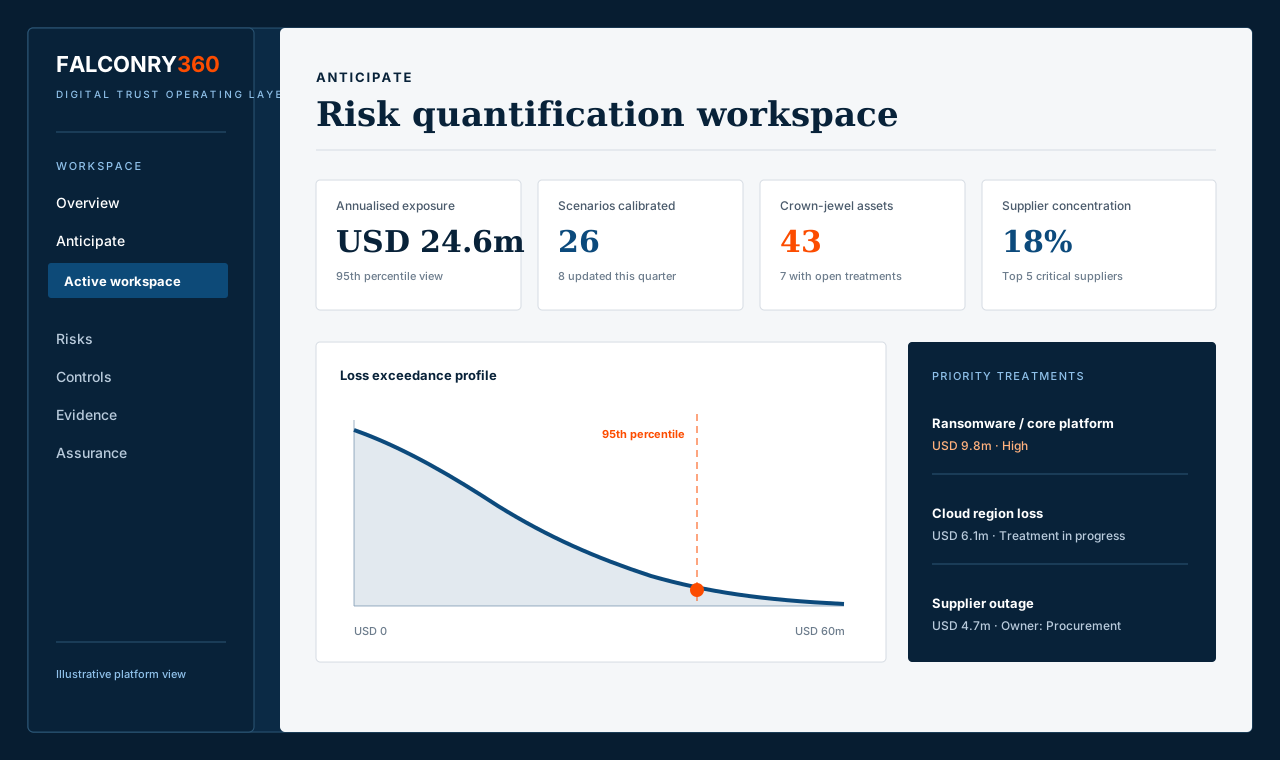 Illustrative platform view
THE ROLE LENS
Anticipate lets the CISO explain exposure in business language, the DPO see where data risk concentrates and the IT Head prioritise the technical work that changes the risk.
Use FAIR-style quantification and calibrated scenarios to compare exposure with the cost and effect of treatment.
Exposure in decision languageConnect processing, transfers, suppliers and incidents to the scenarios that could create regulatory, customer or operational loss.
Privacy risk by contextRank vulnerabilities, cloud concentration, technical debt and supplier dependencies by the exposure they create for important services.
A risk-ranked work queueTier suppliers by criticality, data exposure, substitutability and fourth-party dependency, with treatment actions linked to contracts and services.
Supply chain exposure visibleWHAT THE PLATFORM OPERATIONALISES
Anticipate is where the organisation moves from collecting signals to deciding what matters.
Decompose frequency and magnitude assumptions, run simulations and retain the evidence and confidence behind the estimate.
Maintain severe-but-plausible scenarios for ransomware, cloud loss, supplier outage, insider exfiltration, OT disruption and more.
Assess applications, infrastructure, data, OT and cloud assets in the context of business services and crown-jewel criticality.
Tier suppliers, track data exposure and contract obligations, and view portfolio-level dependency and substitutability.
Map relevant intelligence and findings to assets, techniques, controls and owners so a new signal changes the treatment conversation.
Track AI, cloud, geopolitical, OT convergence and other emerging risks as first-class records with defined treatment paths.
FROM RECORD TO ROUTINE
The platform keeps the assumptions visible so the decision can be challenged and improved.
Ingest signals from assets, suppliers, incidents, intelligence and existing tools.
Set assumptions with practitioners and retain the source and confidence of each input.
Compare loss distributions, appetite and treatment options in a common language.
Route the work to the owner, control, supplier or programme that can change the exposure.
Re-run the model as evidence, controls, incidents or business conditions change.
CONNECTED BY DESIGN
Quantified risk gives Govern a better investment decision, Comply a better priority order, Withstand a better scenario set and Assure a better test plan.
Every exposure can be traced to the records that create it and the controls or decisions that can reduce it.
FalconryX can suggest scenario parameters from approved incident history and asset criticality, then flag assumptions that need practitioner review.
FALCONRYX · GOVERNED AI IN PRACTICE
FalconryX helps teams move from signals to structured scenarios and treatment options while keeping data sources, confidence and professional judgement visible.
A named human reviews and approves.
Use approved asset, incident, threat and supplier records to propose a severe-but-plausible scenario and the business services it could affect.
Human checkpoint · Risk owner confirms scopeFlag unsupported ranges, inconsistent inputs and missing evidence in FAIR-style frequency and magnitude estimates before simulation.
Human checkpoint · Practitioner calibratesSuggest links from a vulnerability, threat or supplier event to assets, services, controls and existing risk scenarios so prioritisation has context.
Human checkpoint · Technical owner validatesPrepare a narrative comparing cost, residual exposure and expected risk reduction using the approved model and treatment assumptions.
Human checkpoint · Leadership selects treatmentFalconryX works within tenant permissions and approved records. Sources and recommendations remain traceable, activity is logged, and no output becomes a decision, formal interpretation or assurance conclusion without named human approval.
REGULATORY AND STANDARDS ANCHORS
Coverage is indicative until the client perimeter is confirmed. The applicable pack, mapping and ownership are agreed during scoping and maintained as the instruments change.