
Services
Managed cyber services
We run the routine — control operation, evidence, assessment cycles, privacy operations and reporting — while your team keeps the decisions and the accountability. Four ways to engage, three service tiers, one accountability line that stays with you.
FALCONRY360 IN PRACTICE
See the operating layer behind the service.
The platform gives the client a current view of the work, not only an end-of-month report. Scope, owners, evidence and actions remain visible between service reviews.
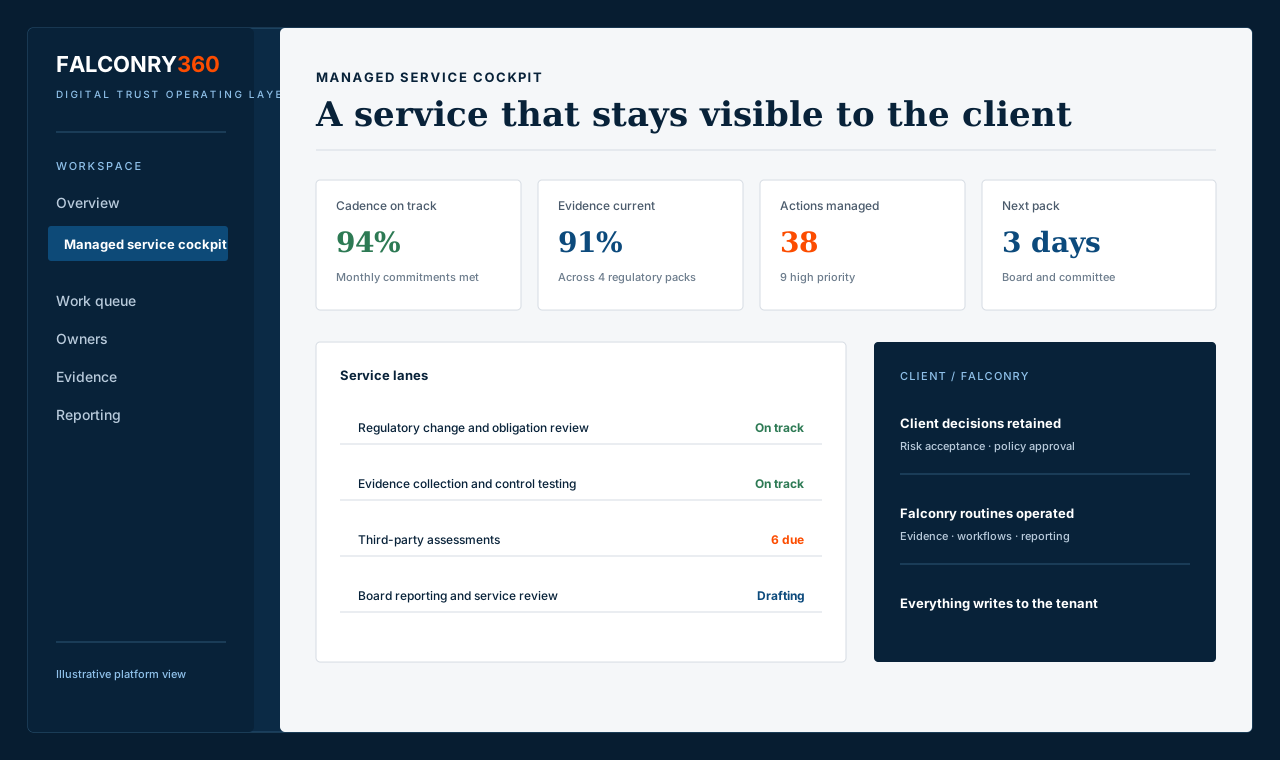 Illustrative platform view
What we operate
All of it inside your tenant, using your control library, with the work visible to you as it happens.
- Compliance operations
- Control testing to schedule, evidence collection and chasing, exception handling, findings tracking and examination response across every regime in scope.
- Regulatory change
- Monitoring, impact assessment and routing to control and policy owners across the markets you operate in.
- Third-party risk operations
- Assessment cycles by supplier tier, evidence review, clause tracking, reassessment scheduling and portfolio concentration reporting.
- Privacy operations
- Records maintenance, rights request handling, DPIA triage, transfer register upkeep and breach workflow.
- Risk operations
- Register maintenance, quantification refresh, scenario calibration and treatment plan tracking.
- Human risk programme
- Phishing simulation waves, role-based awareness delivery, coaching, behaviour scoring and culture measurement.
- Vulnerability coordination
- Findings ingested from your testing providers, deduplicated, assigned, aged and escalated. Coordination and governance, not the testing itself.
- Resilience operations
- BIA cycles, plan currency, dependency map upkeep, exercise scheduling and post-exercise action tracking.
- Incident support
- Retained response support, notification clock management across jurisdictions, evidence capture and post-incident review.
- Reporting
- Board, committee and regulator reporting produced on a fixed cadence from live platform data.
What this is not. We do not operate a security operations centre, and we do not provide detection and response, penetration testing or red teaming. Where you have an MDR or SOC provider we consume their output and govern the outcomes. Where you do not, we will tell you that you need one rather than imply we are it.
Service tiers
Priced in USD, scoped against your regulatory perimeter, estate size and the jurisdictions in play.
TRUST ESSENTIALS
Monitor
The platform running properly, with the routine kept current.
- Platform administration and configuration upkeep
- Regulatory pack maintenance for one jurisdiction
- Evidence collection schedules and chasing
- Control health monitoring and exception reporting
- Quarterly reporting pack
TRUST COMMAND
Operate
The routine run for you, across multiple regimes, with a named team.
- Everything in Essentials, across multiple jurisdictions
- Control testing to an agreed schedule
- Third-party assessment cycles run end to end
- Privacy operations, including rights requests and transfers
- Risk quantification refresh and scenario maintenance
- Regulatory change assessment and routing
- Monthly board and committee reporting
- Named service lead and quarterly service review
TRUST COMPLETE
Command
The function operated as a managed capability, with your accountability intact.
- Everything in Command
- Virtual CISO and virtual DPO capacity
- Examination and audit response run end to end
- Resilience programme, testing and exercises
- Human risk programme and academy pathways
- Incident response retainer and crisis support
- Certification readiness and auditor liaison
Four ways to engage
Designed to be used in sequence rather than chosen between. Most clients arrive with a problem and leave with a system that does not depend on the people who fixed it.
- Consulting
- Advisory on the problem in front of you: regulatory readiness, examination findings, risk quantification design, resilience programmes, privacy operating models, target operating model design. Delivered by practitioners who have held these roles.
- Technology enablement
- Configuring the platform to your organisation — control library, regulatory packs, asset and supplier masters, evidence routines, workflow, reporting and integrations with the tooling you already run.
- Managed services
- We run the routine at the tier you choose, while your team keeps the decisions. Set out above.
- Falconry Academy
- Capability transfer: practitioner development, certification pathways, role-based awareness programmes and CISO-level development, so the capability stays with your people.
Solve
A consulting engagement on the immediate problem. It has to be worth doing on its own terms, whether or not the platform follows.
Systemise
The fix is configured into the platform — controls, mappings, owners, evidence routines and reporting — so it survives the people who made it.
Sustain
Managed services run the routine at the tier you choose, and the academy builds the capability you want to keep in-house.
DELIVERY OPTIONS
Choose the operating model that fits your team.
The platform remains the system of record. The balance between client ownership and Falconry delivery can change as capability matures.
Platform-enabled
Your team runs the programme with Falconry360, Global Libraries and configuration support.
Explore the platform →Co-managed
Falconry operates selected routines—evidence, regulatory change, privacy or resilience—alongside your owners.
Discuss co-management →Fully managed
Falconry runs the agreed service cadence while your officers retain accountability, decisions and risk acceptance.
Discuss managed delivery →