
Run one cyber compliance operating model.
See applicable obligations, mapped controls, evidence gaps, exceptions and overdue actions across entities, technologies and regulatory regimes.
A live, defensible compliance positionPILLAR 3 OF 5 · CYBER COMPLIANCE AND EVIDENCE
Comply gives the CISO a live, evidence-backed position across every regulation and framework in scope. Requirements map to one shared control set, evidence and exceptions stay connected to accountable owners, and regulatory change is visible before the next review.
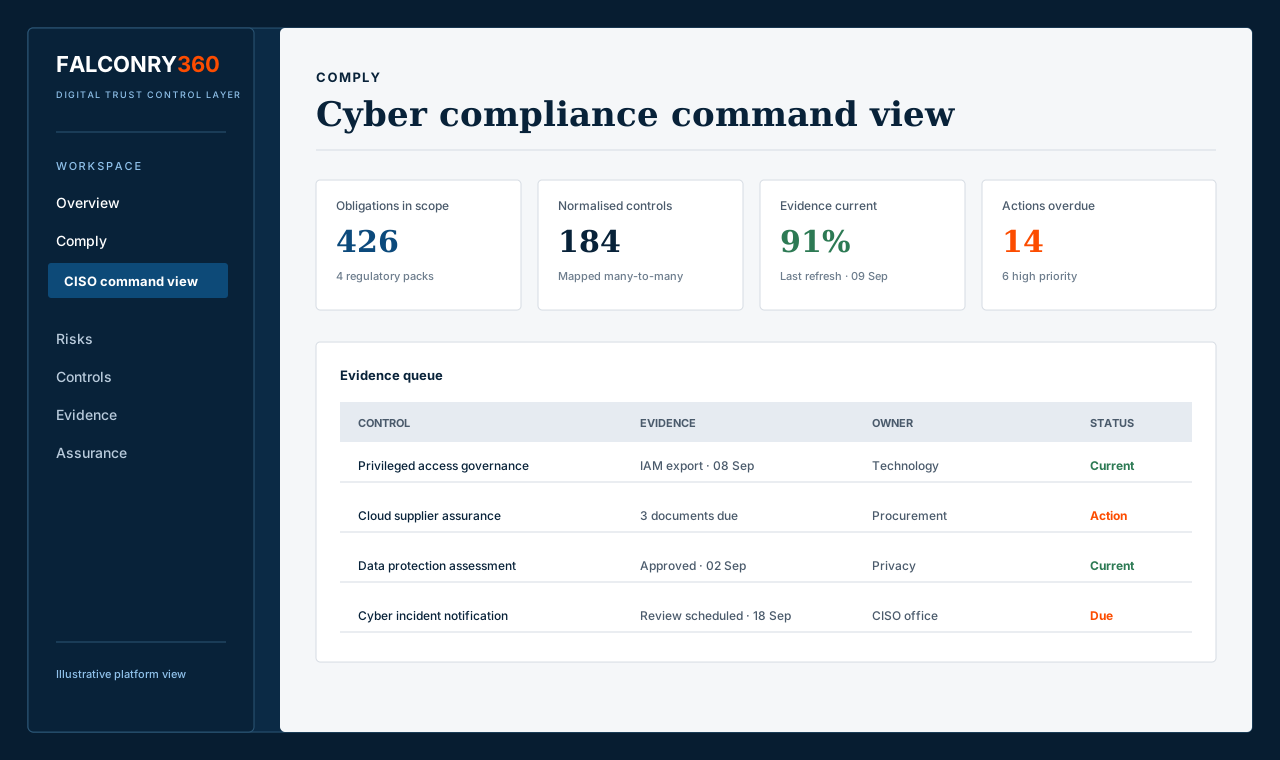 Illustrative platform view
WHO COMPLY SERVES
Comply leads with the CISO's enterprise view across cybersecurity, technology, cloud, privacy, data and third-party obligations. Role-specific workflows let DPOs, IT owners, compliance teams and auditors work from the same governed record without blurring accountability.
See applicable obligations, mapped controls, evidence gaps, exceptions and overdue actions across entities, technologies and regulatory regimes.
A live, defensible compliance positionManage records of processing, DPIAs, rights requests, transfers, retention, consent, incidents and processor evidence against the rules and timelines that apply.
Privacy obligations in operationConnect identity, vulnerability, change, cloud, backup and service-management records to controls so evidence is captured near its source.
Technical evidence without the chaseReview applicability, monitor control performance, test effectiveness and produce scoped responses linked to the requirement, evidence, exception and approval history.
Traceability from clause to conclusionWHAT THE PLATFORM OPERATIONALISES
Comply brings cyber, technology, privacy, third-party and assurance requirements into one control and evidence model—while keeping jurisdictional, sector and contractual differences visible.
Define applicable laws, regulatory instruments and sector requirements by legal entity, jurisdiction, critical service and technology estate, with accountable owners and deadlines.
Manage international standards, certification criteria, customer commitments and internal policies as mapped coverage, clearly separated from regulatory applicability.
Map many obligations to the controls the organisation actually operates, then reuse approved evidence while retaining source, scope, currency and review history.
Operate ROPA, DPIAs, rights requests, data transfers, retention, consent, processor due diligence and breach workflows within the same governed model.
Connect due diligence, criticality, contractual clauses, data exposure, assurance evidence, exceptions and reassessment to the services and controls they affect.
Assess change, identify affected entities and controls, route remediation, and assemble supervisory, audit, certification and customer responses from approved records.
FROM PERIMETER TO PROOF
The operating cycle starts with what applies and ends with a current, evidence-backed position the CISO can explain, challenge and defend.
Confirm entities, jurisdictions, regulators, critical services, technologies and contractual commitments in scope.
Load applicable clauses and relevant frameworks, then map them to normalised controls without erasing genuine local differences.
Give every control, evidence item, review cadence, exception and remediation action a named accountable owner.
Track evidence currency, control performance, gaps, waivers, overdue actions and regulatory change in one view.
Give leaders, regulators, customers and auditors scoped dashboards and response packs linked to approved source records.
CONNECTED BY DESIGN
Falconry360 links assets, risks, obligations, controls, signals, incidents, evidence and assurance. Comply uses that shared model to show not only whether a requirement is mapped, but whether its control is operating, evidenced and independently challenged.
Map once and reuse controls and evidence across requirements. Source obligations and genuine jurisdictional differences remain visible where they matter.
Each role receives its own dashboard, decisions, evidence queue and workflow while leadership sees the consolidated enterprise position.
FALCONRYX · GOVERNED AI IN PRACTICE
FalconryX helps the CISO and compliance team interpret approved source material, assess impact, map obligations, challenge evidence and prepare responses—without turning an AI suggestion into an approved compliance position.
A named human interprets, decides and approves.
Summarise approved source text, effective dates, affected entities, services and obligations, then propose an impact assessment and owner route.
Human checkpoint · Regulatory owner interpretsCompare new clauses with the normalised control library, reuse established mappings where appropriate and keep genuine local differences visible.
Human checkpoint · Control owner approvesCheck whether evidence is current, in scope, attributable and aligned to the mapped requirement, then flag gaps, conflicts and ageing records.
Human checkpoint · Reviewer concludesDraft a regulator, customer, audit or committee response linking each requirement to its control, evidence, exception, owner and approval history.
Human checkpoint · Authorised officer signs offFalconryX works within tenant permissions and approved records. Sources and recommendations remain traceable, activity is logged, and no output becomes a decision, formal interpretation or assurance conclusion without named human approval.
REGULATORY AND STANDARDS ANCHORS
Regulatory applicability is confirmed by legal entity, jurisdiction, sector and service. International standards, assurance criteria and contractual commitments are then mapped as additional coverage—not presented as regulation.
REGULATORY AND SECTOR INSTRUMENTS
INTERNATIONAL AND ASSURANCE FRAMEWORKS
Coverage is indicative until the client perimeter is confirmed. See the framework library or review market coverage.