
Show the mandate in motion.
Translate board appetite into a cyber roadmap, decision queue and executive narrative with evidence behind every material number.
A live cyber mandatePILLAR 1 OF 5 · MANDATE AND ACCOUNTABILITY
Govern turns leadership intent into named owners, agreed appetite, decision records and reporting that the board, regulator and operating teams can all read.
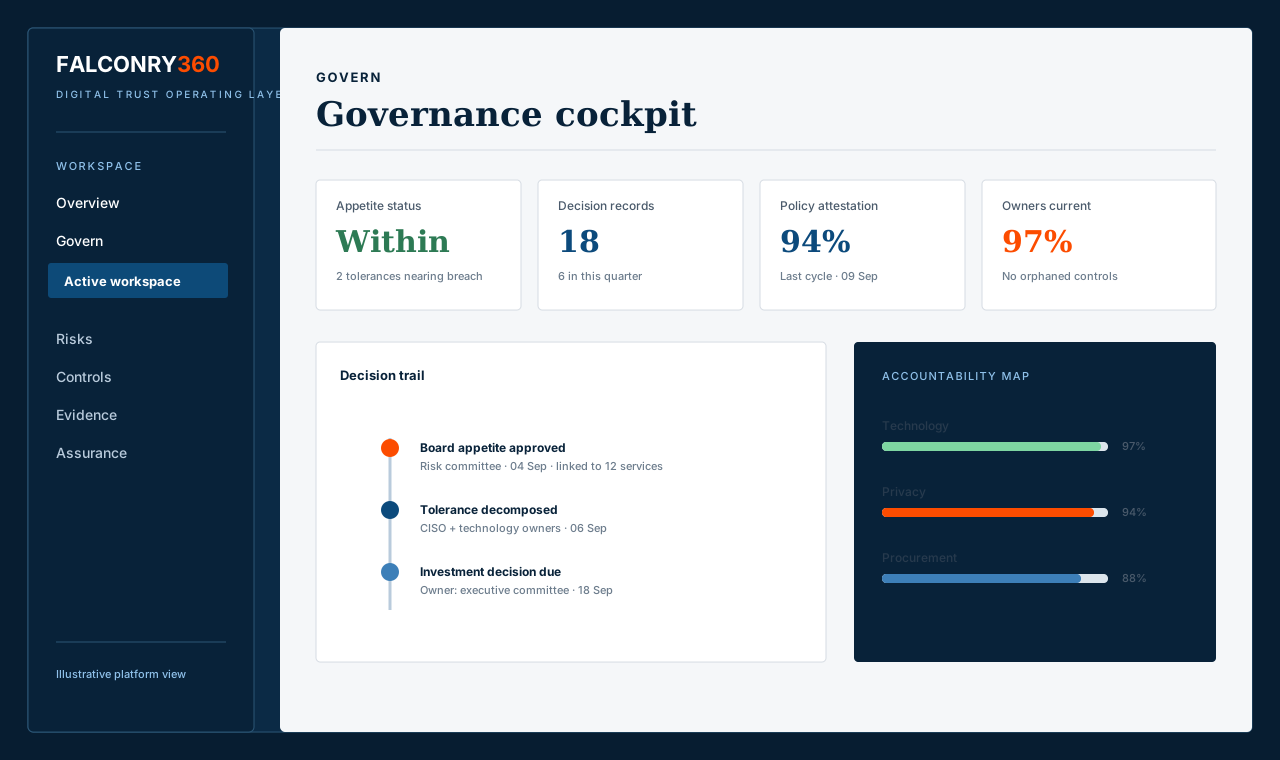 Illustrative platform view
THE ROLE LENS
For the CISO, DPO and IT Head, the question is not whether a policy exists. It is whether the organisation can show who owns the risk, what tolerance applies and what decision is due.
Translate board appetite into a cyber roadmap, decision queue and executive narrative with evidence behind every material number.
A live cyber mandateLink privacy risks, policy approvals, transfer decisions and incident obligations to the governance forums that can resolve them.
Decisions with privacy contextKeep accountability current as services, teams, suppliers and architectures change—without orphaned controls or stale committees.
No orphaned accountabilityReview appetite, exceptions, investment and overdue commitments from a controlled record that can be traced back to source evidence.
A defensible decision trailWHAT THE PLATFORM OPERATIONALISES
Govern is the context layer that makes every other pillar actionable. It holds the mandate, the decision rights and the escalation route.
Terms of reference, delegated authority, three lines and accountable owners held as live records rather than buried in documents.
Set appetite at board level and decompose it into measurable tolerances by service, asset class, risk type or regulatory exposure.
Author, review, approve, publish, attest and retire policies with direct links to the controls they mandate.
Capture the decision, rationale, owner, expiry and impacted records so risk acceptance is never separated from its context.
Tie programmes and investment to the exposure they reduce, the maturity target they support and the regulatory clock they answer.
Assemble board and management views from the live record—exposure, posture, incidents, actions and decisions.
FROM RECORD TO ROUTINE
The platform turns governance from a calendar event into an operating rhythm.
Confirm appetite, scope, decision rights and committee cadence.
Route each risk, control, policy and action to a named accountable person.
Collect attestations, review breaches and keep the decision queue current.
Bring the right evidence, impact and options to the right forum.
Record the decision, action and outcome against the original mandate.
CONNECTED BY DESIGN
A tolerance in Govern becomes a threshold in Anticipate, a requirement in Comply, a service boundary in Withstand and an assurance question in Assure.
Each record carries scope, authority, dates, status and evidence so the organisation can see what changed and why.
FalconryX can draft a regulatory impact assessment or committee narrative from approved records. A named human approves what becomes an official decision.
FALCONRYX · GOVERNED AI IN PRACTICE
FalconryX works across approved governance records to prepare the next decision, expose what needs attention and reduce the administration around committees and policies.
A named human reviews and approves.
Assemble approved posture, appetite breaches, exceptions, exposure and overdue commitments into a first draft with links back to each source record.
Human checkpoint · Pack owner approvesSuggest the obligations, controls, procedures, owners and attestations affected by a proposed policy change before it enters approval.
Human checkpoint · Policy owner validatesIdentify decisions and actions in approved minutes, connect them to impacted risks or controls and prepare routing to named owners.
Human checkpoint · Secretariat confirmsMonitor approved thresholds, delegations and exception expiry dates and surface items that require escalation to the right governance forum.
Human checkpoint · Accountable executive decidesFalconryX works within tenant permissions and approved records. Sources and recommendations remain traceable, activity is logged, and no output becomes a decision, formal interpretation or assurance conclusion without named human approval.
REGULATORY AND STANDARDS ANCHORS
Coverage is indicative until the client perimeter is confirmed. The applicable pack, mapping and ownership are agreed during scoping and maintained as the instruments change.