
Show whether the investment is working.
Link testing results, control health, incidents and risk exposure so the board can see whether treatment changed the posture.
Evidence of effectivenessPILLAR 5 OF 5 · TESTING AND CONFIDENCE
Assure brings control testing, combined assurance, issues, remediation and board reporting onto the same records used to run the programme—so assurance is evidence of how the organisation operates, not a parallel universe.
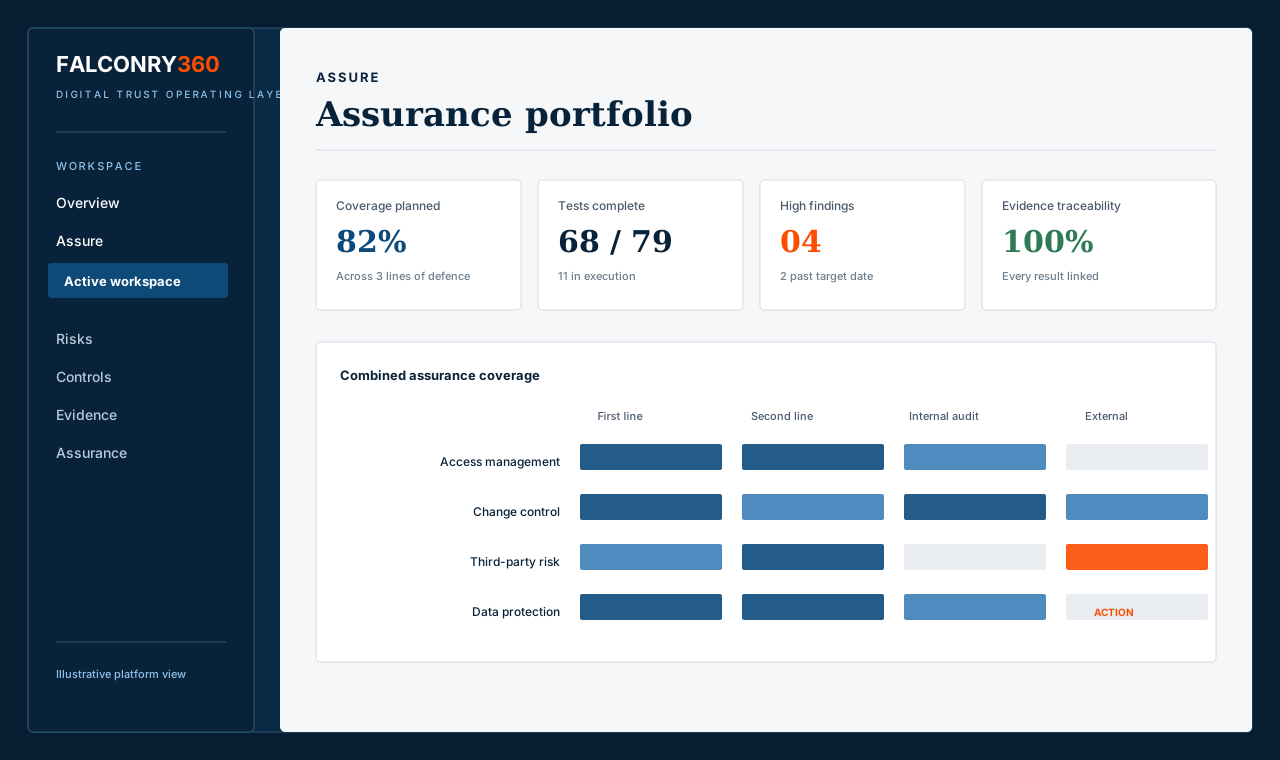 Illustrative platform view
THE ROLE LENS
Assure gives leadership, risk, privacy, IT and internal audit a shared picture of what has been tested, what failed, who owns remediation and what can be said with confidence.
Link testing results, control health, incidents and risk exposure so the board can see whether treatment changed the posture.
Evidence of effectivenessRetain approvals, assessments, rights-request evidence, processor reviews and incident decisions in a traceable assurance trail.
Privacy assurance on demandRoute technical issues to the teams that own the service or control, with ageing, target dates, re-tests and closure evidence visible.
Remediation that stays closedUse management evidence and control history as inputs while retaining independent scope, judgement, testing and reporting.
Combined assurance with independenceWHAT THE PLATFORM OPERATIONALISES
Assure is where the organisation tests the promises it makes—to itself, its board, its customers and its regulators.
Plan design and operating effectiveness testing, sampling, results, exceptions and remediation against the risk that matters.
Map first line self-assessment, second line oversight, internal audit and external assurance to expose gaps and duplication.
Track maturity, KRIs, KCIs and trend against appetite, roadmap and the target state agreed in Govern.
Keep root cause, owner, target date, action evidence, escalation and re-test history on one issue record.
Assemble a current position on exposure, control health, resilience, incidents, regulatory status and overdue decisions.
Answer customer security due diligence, certification and attestation requests from approved, traceable records.
FROM RECORD TO ROUTINE
The test result is not the end of the workflow; it is the beginning of a controlled improvement cycle.
Prioritise tests by risk, obligation, service criticality and existing assurance coverage.
Record method, scope, sample, result, evidence and professional judgement.
Set root cause, accountable owner, target date and the action that changes the outcome.
Validate closure with new evidence and retain the history of the original finding.
Give leadership a traceable position with open risk and decision options visible.
CONNECTED BY DESIGN
A failed test can change a risk estimate in Anticipate, trigger a policy or obligation response in Comply, expose a resilience weakness in Withstand and create a decision for Govern.
The platform preserves the chain from assertion to evidence to remediation, including who approved the conclusion and when.
FalconryX can assemble a first draft of a board pack or regulator response from approved platform records, with every figure traceable to its source.
FALCONRYX · GOVERNED AI IN PRACTICE
FalconryX prepares analysis and drafts from governed records so assurance teams can spend more time challenging evidence, reaching conclusions and influencing remediation.
A named human reviews and approves.
Suggest areas for review using risk exposure, regulatory obligations, service criticality, recent change and existing assurance coverage.
Human checkpoint · Assurance owner sets planPrepare procedures from the control objective, risk and evidence requirement while preserving the tester’s scope and professional judgement.
Human checkpoint · Tester approves methodIdentify stale records, conflicting dates, missing approvals, incomplete samples and evidence that does not support the stated conclusion.
Human checkpoint · Reviewer evaluatesSummarise approved results, combined-assurance gaps, overdue remediation and residual exposure with traceability to the underlying work.
Human checkpoint · Report owner signs offFalconryX works within tenant permissions and approved records. Sources and recommendations remain traceable, activity is logged, and no output becomes a decision, formal interpretation or assurance conclusion without named human approval.
REGULATORY AND STANDARDS ANCHORS
Coverage is indicative until the client perimeter is confirmed. The applicable pack, mapping and ownership are agreed during scoping and maintained as the instruments change.